cambaz
Founder
-
Joined
-
Last visited
Files posted by cambaz
-
Improve Every Aspect of Your WordPress Design: Live, Easy and Fun. Goodbye backend! Design all your forms live, right from the Elementor editor. Choose your fields, increase spacing, set columns and layout... Control everything, all without ever leaving the editor.
-
- 0 Downloads
Updated -
- 0 Downloads
Updated -
Precracked, with no callbacks removed, so operate at your own risk, but the license is valid and comes fully featured. If you avoid connect features you should be fine.
When it asks for a key when installing or upgrading, you can put anything you'd like, and it'll take it. -
DNS Over HTTPS
Alongside the default HTTPS connections, Badger's DNS over HTTPS provides usability of newly bought domains without the the need of domain fronting or redirector, all the while providing a backup option to be able to switch to other HTTPS profiles on the fly
External C2 Channels
The SMB and TCP badger provide functionality to write custom External C2 Channels over legitimate websites such as Slack, Discord, Microsoft Teams and more
Indirect Syscalls
Badger provides various process injection capabilities and an option to switch between WinAPI to NTAPI to Syscalls on the fly
Built-in Debugger To Detect EDR Userland Hooks
Badger provides various techniques to hunt EDR userland hooks and DLL, and avoid triggering them using various syscall obfuscation and debugging techniques
Brute Ratel MITRE graph
Brute Ratel features a seamlessly integrated MITRE graph for all built-in commands providing a user friendly interface for Adversary Simulation activities
One stop for all your LDAP queries
Ldap Sentinel provides a rich GUI interface to query various ldap queries to the Domain or a Forest. Whether you want to run SPN queries for a specific user or if you want to query large group objects, all can be done effortlessly using prebuilt queries.
Multiple Command and Control Channels
Badger provides mulitple pivot options such as SMB, TCP, WMI, WinRM and managing remote services over RPC.
Automate Adversary TTPs
Use existing brute ratel modules or build your own using in-memory execute of C-Sharp, BOFs, Powershell Scripts or Reflective DLLs and automate the execution of the commands using the Click Script feature
Various Out-Of-Box Evasion Capabilities
Evasion Capabilities
x64 Support
x86 Support
x86 on Wow64 Support
Stack Frame Chaining
Yes
No
No
Indirect System Calls
Yes
Yes
Yes
Hide Shellcode Sections in Memory
Yes
Yes
Yes
Multiple Sleeping Masking Techniques
Yes
No
No
Unhook EDR Userland Hooks and Dlls
Yes
No
No
Unhook DLL Load Notifications
Yes
No
No
LoadLibrary Proxy for ETW Evasion
Yes
No
No
Thread Stack Encryption
Yes
Yes
Yes
Badger Heap Encryption
Yes
Yes
Yes
Masquerade Thread Stack Frame
Yes
Yes
Yes
Hardware Breakpoint for AMSI/ETW Evasion
Yes
Yes
Yes
Reuse Virtual Memory For ETW Evasion
Yes
Yes
Yes
Reuse Existing Libraries from PEB
Yes
Yes
Yes
Secure Free Badger Heap for Volatility Evasion
Yes
Yes
Yes
Advanced Module Stomping with PEB Hooking
Yes
Yes
Yes
In-Memory PE and RDLL Execution
Yes
Yes
Yes
In-Memory BOF Execution
Yes
Yes
Yes
In-Memory Dotnet Execution
Yes
Yes
Yes
Network Malleability
Yes
Yes
Yes
Built-In Anti-Debug Features
Yes
Yes
Yes
Module stomping for BOF/Memexec
Yes
Yes
Yes -
These files are required to use developer mode in IPS Community Suite.
- 0 Downloads
Submitted -
Some of the changes in XF 2.3.12 include:
Merge class extensions for repository classes registered under both their stripped alias and suffixed name
Route RSS feed fetches through the untrusted HTTP reader
Fix xf:file-clean-up deleting excluded files (e.g. hashes.json)
Current requirements
Please note that XenForo 2.3 has higher system requirements than earlier versions.
The following are minimum requirements:
PHP 7.2 or newer (PHP 8.3 recommended)
MySQL 5.7 and newer (Also compatible with MariaDB/Percona etc.)
All of the official add-ons require XenForo 2.3.
Enhanced Search requires at least Elasticsearch 7.2.
-
- 0 Downloads
Submitted -
This is a modified version of Cheat Engine 7.4; all strings and similar elements related to Cheat Engine have been altered. It uses a different driver and goes undetected by many games and programs.
-
This is a trial removal tool compatible with all versions of Eazfuscator; it removes the trial version from files packaged with the Eazfuscator demo.
How to use:
- Drag and drop the packaged demo exe onto the trial remover; that's all there is to it. -
This version has been modified to avoid detection by Process Hacker; the strings, title, and driver have been changed
-
This is a modified version of x64dbg and x32dbg that is undetectable by classic anti-debugger mechanisms; if you still encounter anti-debug errors, use TitanHide or HyperHide.
-
-
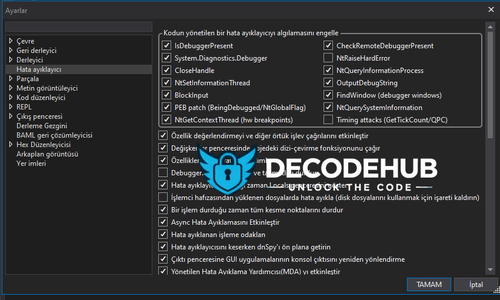
HTTP Debugger – Undetected Version
HTTP Debugger is a debugging tool that allows you to analyze incoming and outgoing data over an internet connection and send custom/fake responses.
This version has been modified by our team. The following changes have been made:
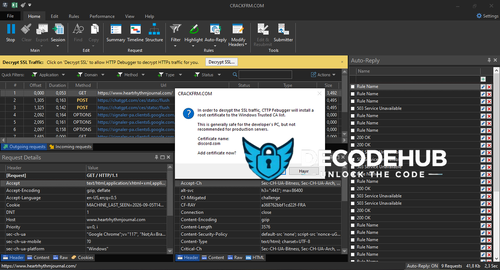
The certificate has been replaced with a trusted root certificate.
All strings have been completely modified.
The driver file has been modified.
The SDK has been modified.
Installation
Install all .reg files included with the release.
Add the discord certificate file to your Trusted Root Certification Authorities.
Copy cttpfdebuggersdk.sys into the System32 directory.
To install and start the service, open CMD as Administrator and run the following command:
sc create crackfrmcomudds binPath= "C:\FilePath\crackfrmcomSvcc.exe" start= auto DisplayName= "crackfrmcomudds" Replace C:\FilePath\ with the actual location of crackfrmcomSvcc.exe.
This command creates the service and configures it to start automatically.
Enter the following command to start the service, and then launch the debugger:
sc start crackfrmcomudds